What's inside
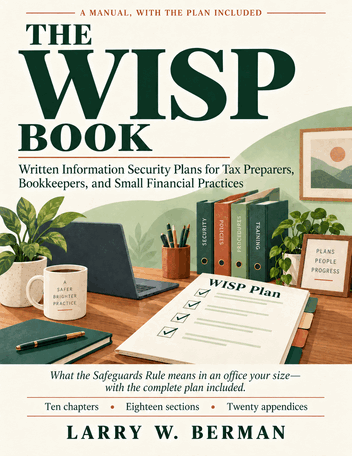
A manual, with the complete plan in it. The first half explains what the rules actually require of a small practice. The second is the plan itself — eighteen sections you adopt, and twenty appendices that hold the proof you did the work.
Part One — the translation#
Chapters that take each requirement and answer the only question that matters in a four-person office: what does this mean for us, specifically?
The regulation says you must designate a Qualified Individual. Fine — but can it be you, if you are also the person doing the returns, and what happens when you are on vacation in April? It says you must encrypt customer information at rest and in transit. What counts as encrypted, and does that mean you can never email a client a document again? It says you must oversee your service providers. Your tax software is made by a company that will not negotiate a contract with you; now what?
Part One works through these. Where the answer is a judgment call rather than a rule, it says so, and gives you the considerations rather than a false certainty.
Three considerations, treated at length#
- The small-firm exception. Fewer than 5,000 consumers excepts you from four specific requirements. Whether to rely on that is a strategic choice with consequences either way — and the arithmetic of who counts as a consumer is not what most people assume.
- The breach clocks and the encryption safe harbor. What encryption does and does not protect you from, and why it does not stop the first phone call.
- The third consideration, which follows from the first two.
Build in order, not all at once#
A chapter on sequence. If you have nothing today, the order you do this in determines whether you finish. It gives you the dependencies, rough time estimates, and what to do first — which is not the thing most people start with.
Part Two — the plan itself#
A complete Written Information Security Plan in eighteen numbered sections, written to be filled in and adopted rather than admired. Each section traces to the provision it satisfies, and each names the appendix that proves it was done.
It is not a sample. It is drafted to be the real thing, with the customization points marked in brackets so you can see exactly where your firm's judgment goes.
The twenty appendices#
This is the half that most templates skip, and it is the half that matters when someone asks you to demonstrate anything. Appendices A through T are the evidence system: the forms, logs, registers, and signed acknowledgments that turn “we do that” into something you can put on a table.
Breach response
The notification card, worked row by row — who to notify, at what count, on what clock, measured against whom.
Device and encryption records
What hardware holds client data, how each device is encrypted, and whether its recovery key is held and where. Never the key itself.
Service provider register
Who can reach your data, and what each one is contractually required to do about it — including the large platforms whose terms of service are the written assurance.
Testing regime election
A place to record which testing position your firm has taken and why, so following the book's own advice does not leave a blank page in your plan.
Disposal and retention logs
What was destroyed, when, by what method, and under whose certificate — tied to the current sanitization standard, not the withdrawn one.
Annual and quarterly reviews
The revisit schedule and the regulatory monitoring check, including where to look up your own EFIN and PTIN activity.
Every appendix carries a certification block, and the wording is deliberate. It certifies that the record is accurate — not that every item was in compliance. That distinction exists so that you can log a deficiency honestly and still sign your name. A form that punishes candor produces dishonest forms.
A note on currency#
The book quotes laws and standards that change. Rather than pretend otherwise, it carries a dated statement of what was verified and when, three specific re-check instructions, and the address of the status page on this site, where each authority is tracked individually.
That address is printed in the book. It is a commitment: that page stays alive and dated for the life of the print run.
The full table of contents#
Printed here in full, because a book that asks you to check dates and sources should let you see exactly what you are buying before you buy it.
The book
| Part I — Context | 1. Why This Document Exists 2. The Anatomy of a WISP |
|---|---|
| Part II — The Sections and Their Proof | 3. Who Owns the Plan 4. Knowing Your Office 5. The Safeguards 6. People and Vendors 7. When Things Go Wrong |
| Part III — Assembly | 8. The Appendix System 9. The Crosswalk 10. A Living Document |
| Considerations | 1. The Small-Firm Exemption: Claim It or Waive It 2. The Clocks, Side by Side 3. Will You Outgrow This Plan? |
| Sources and Authorities | The primary authorities, then every source organized by chapter, then A Note on Currency |
The plan — eighteen sections
1. Program Governance & Purpose · 2. Qualified Individual Designation · 3. Scope & Applicability · 4. Definition of Protected Information · 5. System & Data Inventory · 6. Data Flow Description · 7. Risk Assessment · 8. Administrative Safeguards · 9. Technical Safeguards · 10. Physical Safeguards · 11. Access Controls & Authentication · 12. Encryption Policy · 13. Vendor Management · 14. Training & Awareness · 15. Incident Response Plan · 16. Backup & Recovery · 17. Secure Disposal & Retention · 18. Review, Monitoring & Enforcement
The plan — twenty appendices
Preceded by the Cross-Reference Map, which puts every section beside the appendix that proves it.
| A | Security Compliance Checklist |
|---|---|
| B | Security Incident Report & Response Log |
| C | Backup Verification & Encryption Log |
| D | Computer & Device Inventory Log |
| E | Network Map & Router Security Documentation |
| F | Access Control & User Account Log |
| G | Vendor & Service Provider Security Review Log |
| H | Security Awareness Training Log |
| I | Risk Assessment Worksheet |
| J | Patch & Update Verification Log |
| K | Secure Disposal Log |
| L | Remote Access Authorization Log |
| M | Password & MFA Acknowledgment |
| N | Testing, Monitoring & Incident Simulation Log |
| O | Business Continuity & Disaster Recovery Summary |
| P | External Device Control & Exception Log |
| Q | Printer & Scanner Inventory Log |
| R | Annual WISP Review & Management Acknowledgment |
| S | Mandatory Ongoing WISP Tasks Checklist |
| T | Workforce Confidentiality & Access Agreement |
Details#
| Full title | The WISP Book: Written Information Security Plans for Tax Preparers, Bookkeepers, and Small Financial Practices |
|---|---|
| Edition | Second edition (Datum) |
| Format | Paperback — 190 pages |
| ISBN-13 | 979-8-175-62681-1 |
| Appendices | Twenty, A through T |
| Plan sections | Eighteen |
| Review rounds before publication | Twelve — the record |